$ whoami
The short version: I'm Robert. I run enterprise security infrastructure for a living, and this site is where the field notes go.
the long version
I've been in IT for fifteen years, and I've held most of the jobs this industry offers on the way up: NOC operator, help desk, communications technician at a small hospital system. From there, four years of network engineering, then a move to network security at the same organization — the classic path of the person who kept asking the firewall team too many questions.
Next came a large healthcare organization, first as a cybersecurity specialist and then as a senior cybersecurity specialist, where my team ran the firewalls — hundreds of them, across the US and several other countries — plus the remote-access stack and the tools that manage firewall policy. While I was there I led the replacement of the legacy remote-access solution with a cloud secure web gateway and private-access platform, so I've deployed an SSE stack from one vendor before running one from another. That doesn't bias my opinion — every tool has its pros and cons, and I've lived with both.
Today I'm a security engineer at a large tech company, where I run our SSE platform end to end — secure web gateway, private access, the device agent, digital experience monitoring — serve as the point person reviewing network access requests for my side of the network, and manage the enterprise browser. When something between the user and the internet breaks, my day gets interesting.
the name
any any deny is the rule at the bottom of every sane
firewall policy: source any, destination any,
action deny. Whatever the rules above didn't explicitly
allow gets dropped. It's the default posture this entire industry
is built on — deny by default, allow on purpose.
And it sure beats the alternative. If you've ever found an any-any-ALLOW living quietly in a production policy, you know the feeling. Some of us actively hunt for those.
why this site exists
The moment this site comes from: a business-critical tool broke, company-wide, all at once. One query in the SIEM showed me what happened and why — a vendor URL miscategorization had exposed a mistake in a PAC file, a bypass that was written incorrectly — and the fix took minutes. Finding anything written down about that failure mode took longer than the outage did.
That's the pattern: the knowledge that fixes these problems lives in people's heads and dies in closed tickets. The official docs stop one step before the part that's actually broken, and the forum thread ends in "nvm, fixed it."
Here's the thing — coworkers have teased me for years about how verbose my ticket notes are. When I work a problem, I write down everything: what changed, screenshots, the dead ends, all of it. Work notes stay at work, and nothing on this site comes from them. This site is the same write-it-down habit pointed at general knowledge instead: how these technologies behave in any environment, straight from the docs and the lab. I came up from the help desk and learned a lot of this from people who took the time to write things down. This is me doing the same.
the tools
Every tool on this site is something I built because I needed it. They run entirely in your browser — no accounts, no uploads, no tenant connections, nothing leaving your machine. Don't take my word for it: view source and check.
I'm not selling a platform. I'm a security engineer who makes tools I actually use, shared with a community that's given me plenty.
for the cert-checkers
(I'd check too.) Current alphabet: CISSP, CCSP, SSCP, ZDTA, ZDTE, along with a bachelor's and a master's in cybersecurity. There's also a stack of older ones from the climb — CEH, incident handling, Check Point CCSA, the full CompTIA run, ITIL. Some of those have expired along the way, but they show you the road I took.
off the clock
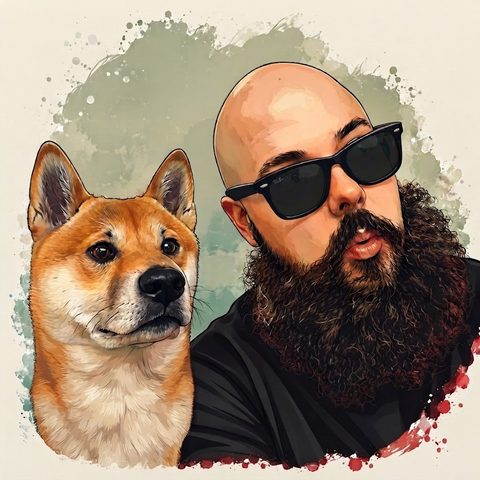
Powered by a coffee setup that has gotten completely out of hand, a lifetime of gaming, and a Shiba Inu escape artist who has defeated every containment control I've ever deployed.
contact
Something broken? Something wrong in a post? Something you want covered? robert@anyanydeny.com. Corrections are especially welcome — this site trades on being right, not on being first.
get the field notes
Occasional troubleshooting write-ups and tool launches. No spam, no vendor pitches, unsubscribe anytime.
ack — check your inbox for a confirmation link.
One confirmation email, then you're in. Unsubscribe anytime.